Wednesday, August 31, 2016
How Can You Remove Playnow.7113656.com Ads - Adware Removal Guide
If http://playnow.7113656.com and its ads keep redirecting your browser, it means your computer is infected with an adware program. This playnow.7113656.com pop-ups can be bundled with other free software that is downloaded via Internet without your knowledge. With this annoying program installed, the ads from playnow.7113656.com will arbitrarily pop up when you browse the Internet. In considering computer security, it is important to remove the adware program completely and immediately.

Monday, August 29, 2016
How to Remove Awesomeredirector.com Adware - Removal Help Step by Step
If your browser is redirected to unknown website and your favorite homepage keeps turning into http://awesomeredirector.com then there is very likely that your computer is infected with an unwanted adware program. In this post, you will learn how to remove awesomeredirector.com pop-up ads or any other computer infections. Let’s check out there.
Classified as malware, awesomeredirector.com is utilized to increase web traffics for its sponsored websites. Usually, it shows numerous pop-ups within browsers like Edge, Chrome, Mozilla Firefox and Internet Explorer. Then, it resets windows proxy and DNS setting out of users’ attention. Since it is used to promote third parties, you will be directed to adverting sites that include different products or services displaying in various forms like pop-up windows, boxes, in-text ads, different sized banners and so on. Although those ads seem attractive, you should realize awesomeredirector.com is a computer infection and please stay away from it. Remember that it gets access to your PC only attempting to help its owner generate revenue. What's worse, your sensitive information would be invaded with awesomeredirector.com virus inside your computer system. Hence, take proper solution to get rid of this adware program immediately.
Classified as malware, awesomeredirector.com is utilized to increase web traffics for its sponsored websites. Usually, it shows numerous pop-ups within browsers like Edge, Chrome, Mozilla Firefox and Internet Explorer. Then, it resets windows proxy and DNS setting out of users’ attention. Since it is used to promote third parties, you will be directed to adverting sites that include different products or services displaying in various forms like pop-up windows, boxes, in-text ads, different sized banners and so on. Although those ads seem attractive, you should realize awesomeredirector.com is a computer infection and please stay away from it. Remember that it gets access to your PC only attempting to help its owner generate revenue. What's worse, your sensitive information would be invaded with awesomeredirector.com virus inside your computer system. Hence, take proper solution to get rid of this adware program immediately.
Wednesday, August 3, 2016
Redirected by Superhub.7112138.com - How to Remove a Browser Hijacker
The Superhub.7112138.com has been classified as a dangerous browser hijacker / search redirecting virus that you need to avoid and remove once it is traced on your computer. The reason for why it needs to be eliminated is because this hijacker is capable of modifying web browser settings and injecting malicious code in almost every web page, the user has visited. The malicious code tries to monetize the hijacked browsers by showing lots of ads to all the infected browsers. Furthermore, the code will also allow Superhub.7112138.com to continue overriding browser settings, making the recovery nearly impossible by using the conventional methods.
You should know that superhub.7112138.com is an illegitimate webpage that tricks users by promoting spam sponsored links or web pages which can be risky. And then urges users to download or purchase products from these links and make money likewise. Superhub.7112138.com will suddenly occur on your computer screen and state that your Java or Media Player is outdated. However, you should know all this is fake message. And this browser hijacker can do more harm to the infected computer.
You should know that superhub.7112138.com is an illegitimate webpage that tricks users by promoting spam sponsored links or web pages which can be risky. And then urges users to download or purchase products from these links and make money likewise. Superhub.7112138.com will suddenly occur on your computer screen and state that your Java or Media Player is outdated. However, you should know all this is fake message. And this browser hijacker can do more harm to the infected computer.
Thursday, July 14, 2016
Help at Removing Jnd.neonatalcomply.com Pop-ups - Adware Removal Guide
Is your web browser having the redirection issue with Jnd.neonatalcomply.com? Are you feeling annoyed with the pop-up advertisements from Jnd.neonatalcomply.com? Do you want to prevent your browser from being randomly redirected to the http_//jnd.neonatalcomply.com page? If yes, please follow this complete adware removal instruction to remove pop-ups and unwanted advertisements from your computer.
Jnd.neonatalcomply.com is detected as an adware program with the features of displaying numerous ads. It is bundled with other free software that you download off of the Internet. The pop-ups shown are random and they may sometimes contain a Technical Support scam trying to trick you into calling a Support Scam telephone number to fix the problem you experience. You should not call them, of course, because they won’t help you and are very expensive. The proper reaction to Jnd.neonatalcomply.com is take effective solution to remove Jnd.neonatalcomply.com pop-ups as soon as possible.
What is Jnd.neonatalcomply.com?
Jnd.neonatalcomply.com is detected as an adware program with the features of displaying numerous ads. It is bundled with other free software that you download off of the Internet. The pop-ups shown are random and they may sometimes contain a Technical Support scam trying to trick you into calling a Support Scam telephone number to fix the problem you experience. You should not call them, of course, because they won’t help you and are very expensive. The proper reaction to Jnd.neonatalcomply.com is take effective solution to remove Jnd.neonatalcomply.com pop-ups as soon as possible.
Thursday, July 7, 2016
How to Remove Isearch.tinyresults.com from 1stBrowser by SIEN?
Isearch.tinyresults.com is categorized as a browser hijacker that performs unpleasant behaviors to disturb computer users’ surfing experience. This site uses an appealing user interface like the following screenshot, but it will not only replace your favorite search engine and homepage but also display sponsored links and advertisements instead of the regular search results. If you are also in the trouble with Isearch.tinyresults.com and look for effective removal guide to terminate all ads from this nasty browser hijacker, please go ahead to read the following articles.

Tuesday, June 28, 2016
How to Remove Backdoor.PinkSlipBot Trojan - Effective Removal Guide
Backdoor.PinkSlipBot is a Trojan that is involved in spear phishing attacks, capable of stealing into your computer with diverse propagation paths. It also has the alias such as: Trojan/Win32.Qakbot (AhnLab), W32/Trojan.XBYW-8720 (Command),Trojan.Win32.Bublik.ctep (Kaspersky), winpe/Kryptik.CEIY (Norman), Crypt3.AMDJ (AVG),TR/Kazy.442004 (Avira), BackDoor.Qbot.222 (Dr.Web), Win32/Qbot.BH trojan (ESET), W32/Bublik.CTEP!tr (Fortinet), Trojan.Win32.Bublik (Ikarus), TROJ_SPNR.03J714 (Trend Micro).
If the system got infected with such Trojan it will put the system at high risk and install unwanted program within the targeted system. The Backdoor.PinkSlipBot Trojan is designed to exploit the Network Location Awareness service of Windows to recognize connected devices and provide its operators with detailed information about the infected computer. The Backdoor.PinkSlipBot Trojan can run on 32-bit and 64-bit architectures and allow remote code execution on Windows XP, Vista, 7, 8 and 10. The Backdoor.PinkSlipBot Trojan is similar to other Backdoor Trojans, it might disable components of the Windows Firewall to enable its operations. The Win32/Htbot.C Backdoor Trojan might use a corrupted file named svchostcenter.exe to establish an Internet connection to its 'Command and Control' server and receive instructions.
If the system got infected with such Trojan it will put the system at high risk and install unwanted program within the targeted system. The Backdoor.PinkSlipBot Trojan is designed to exploit the Network Location Awareness service of Windows to recognize connected devices and provide its operators with detailed information about the infected computer. The Backdoor.PinkSlipBot Trojan can run on 32-bit and 64-bit architectures and allow remote code execution on Windows XP, Vista, 7, 8 and 10. The Backdoor.PinkSlipBot Trojan is similar to other Backdoor Trojans, it might disable components of the Windows Firewall to enable its operations. The Win32/Htbot.C Backdoor Trojan might use a corrupted file named svchostcenter.exe to establish an Internet connection to its 'Command and Control' server and receive instructions.
Tuesday, May 24, 2016
Quick Way to Get Rid of RDN/YahLover.worm!055BCCAC9FEC
I have this RDN/YahLover.worm!055BCCAC9FEC on my PC, it has been there for about a week and now the problem is out of control. I am using my ipad now, when I restarted my PC this morning, it came to be a black screen and mouse pointer. What can I do to remove this RDN/YahLover.worm!055BCCAC9FEC? Any help will be greatly appreciated!!
Above is a complaint from one of the victims of RDN/YahLover.worm!055BCCAC9FEC. Considering that this infection may have thread many computer users, we write this article to introduce more information about it, and provide you instructions to remove it.
Automatically remove it now! Click this picture to download.

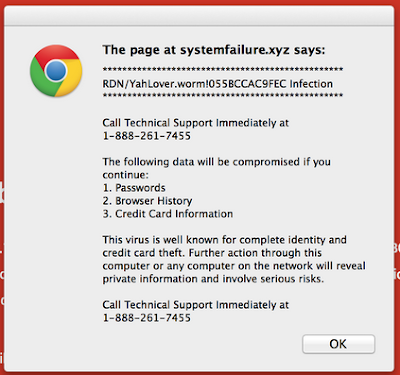
RDN/YahLover.worm!055BCCAC9FEC pop-up comes from the Systemfailure.xyz website which is malicious. In the pop-up window, you can see "RDN/YahLover.worm!055BCCAC9FEC Infection", "Call Technical Support Immediately at 1-888-261-7455", etc.. Once infected, the computer system will be in a total mess. It can makes many changes in the background. For example, it may modify the DNS settings and LAN settings, and theses changes make it impossible to get internet connection. What's more, changes of the settings make it possible for other malicious programs to get on the computer, and cause more security vulnerabilities, putting the computer at risk.
Above is a complaint from one of the victims of RDN/YahLover.worm!055BCCAC9FEC. Considering that this infection may have thread many computer users, we write this article to introduce more information about it, and provide you instructions to remove it.
Automatically remove it now! Click this picture to download.

Know more about RDN/YahLover.worm!055BCCAC9FEC pop-up
RDN/YahLover.worm!055BCCAC9FEC pop-up comes from the Systemfailure.xyz website which is malicious. In the pop-up window, you can see "RDN/YahLover.worm!055BCCAC9FEC Infection", "Call Technical Support Immediately at 1-888-261-7455", etc.. Once infected, the computer system will be in a total mess. It can makes many changes in the background. For example, it may modify the DNS settings and LAN settings, and theses changes make it impossible to get internet connection. What's more, changes of the settings make it possible for other malicious programs to get on the computer, and cause more security vulnerabilities, putting the computer at risk.