Monday, April 28, 2014

How to Remove Trojan Horse PSW.Generic11.CIZG Completely and Safely-Manual Removal Guide

Basic Information on Trojan Horse PSW.Generic11.CIZG


Do you know more about Trojan Horse PSW.Generic11.CIZG? Trojan Horse PSW.Generic11.CIZG is classified as the Trojan horse infection which is firstly reported by AVG and classified it as a high risk threat. How come it gets into your computer without your knowledge? Firstly, it can get itself bundle with the free software downloads or embed its malicious codes onto the spam email attachments, therefore, you may be infected by this malicious virus via downloading free software without paying attention to the default installation of the free software or visiting questionable websites frequently. after it get itself installed on your computer, it can add the registry to the startup items to make itself automatically run every time you launch your computer. Thus, it would be better to keep your antivirus up to date to avoid the virus attack.

What can Trojan Horse PSW.Generic11.CIZG do on your computer?

  • It can alter your default system settings and bypass the antivirus to get into your computer.
  • Unexplained system crash or blue screen.
  • It can operate on your computer backdoor to monitor your online traces or even steal your personal information, which will violate your privacy and put your personal information in danger.
  • It can take up your system resource and then degrade your overall computer performance.
  • It will make your system vulnerable for other malware.

Saturday, April 26, 2014

How to Remove Trojan Horse Generic36.FGM Completely-(Virus Removal Guide)

Brief Description of Trojan horse Generic36.FGM


Recently many computer users reported that they keep receiving warning message from AVG stating that Trojan horse Generic36.FGM error but AVG failed to pick up this Trojan horse infection. It is designed by cyber hackers to generate profit from it. To achieve its purpose, it operate on your computer backdoor to track and store your online traces to report to the remote server, which will violate your privacy and may steal your personal information in danger.

To remove this Trojan horse Generic36.FGM infection, many computer users have tried many ways to get rid of it but all get no luck. For example, they have tried to run MalwareBytes or do a system restore but keep getting error message like 'Windows has detected file system corruption on (C:)” besides, control panel or task manger is also can help to clean up this virus for it can disguise its related files

What Does Trojan Horse Generic36.FGM Do on Your Computer?


  • It can occupy your CPU usage to degrade your overall computer performance.
  • It can add the registries to the startup items so that it can active itself every time you launch your computer.
  • It can operate on your computer backdoor to invite other malware to come into your computer.
  • Unexplained system crash.

How to Remove Alert-government-control.com Manually and Completely-Manual Removal Guide

Alert-government-control.com Description

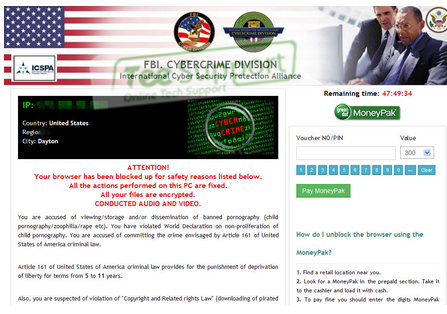
Alert-government-control.com is classified as the fake FBI ransomware which pretends to be genuine government warning stating that you have violated some local laws and needs to pay for it to unlock your computer. With this Alert-government-control.com on your computer, you cannot close the fake FBI warning window. However, if you pay for the ransomware, does it help to get rid of this ransomware virus? I am afraid not, this fake FBI virus will just keep coming back again and again. Therefore, we have no reason to pay for the scam which will just rip off your money.

Wednesday, April 23, 2014

How to Remove Adware Generic_r.EZ Completely and Safely-Manual Removal Guide

Brief Description of Adware Generic_r.EZ


Adware Generic_r.EZ is classified as an adware or potentially unwanted program which can compatible with almost all the popular web browser like Internet Explorer, Firefox, Google Chrome, Safari, etc. Adware Generic_r.EZ can be detected by legitimate antivirus but cannot be completely removed by the program. Adware Generic_r.EZ always bundle with the free software downloads or online games downloads or get into your computer via opening spam email attachments, sharing malicious files with other users online, using infected external hard drive, etc. therefore, Tee Support labs suggest always pay attention to the default installation of the free software and not to visit the questionable websites frequently and use the stable antivirus and remember to keep antivirus up to date.

Since this tricky Adware Generic_r.EZ can disguise its related files on your computer, therefore, control panel or task manager also failed to pick up this tricky adware. As we all know, Adware Generic_r.EZ is designed by cyber hackers to increase web traffic and generate profit from it, to achieve its purpose, it can track and store your online traces like search keywords, favorites, book marks or browser history to violate your privacy and may steal your personal information. Keep it longer, it is also capable to slow down your overall computer performance and display you unstoppable pop up ads or even turn your text into hyperlink and redirect you to other unsafe websites. to completely remove this annoying adware, you are welcome to follow the removal guide listed below:

Monday, April 21, 2014

How to Remove W32.Mezit!inf Completely and Safely-Manual Removal Guide

What Is W32.Mezit!inf? Is It Dangerous?


W32.Mezit!inf is classified as new released Trojan horse which can target all the windows based system and perform malicious activities on your computer. To live with this W32.Mezit!inf, your computer will run slowly and weirdly, you may encounter the symptoms like below:

Computer keeps shutting down itself and run slower and slower than before.
 

Norton360 has detected W32.Mezit!Inf. However, the required action states "requires manual removal".

W32.Mezit!inf can take advantage of your system vulnerability to bypass the antivirus or windows firewall to sneak into your computer without your knowledge. After it get itself installed on your computer, it can add the registries to the startup items so that it can run automatically every time you launch your computer. With this W32.Mezit!inf operate on your computer, it can corrupt your default browser settings and make your system vulnerable for other virus.

How to Remove Checkpcinstant.com Completely-Manual Removal Guide

Know More about Checkpcinstant.com


Checkpcinstant.com is designed by cyber hackers to promote their remote service. With this Checkpcinstant.com on your computer, it can always pop up to remind you that your computer have been infected and you will be asked to paid for the removal service to remove the infection. Actually, it is just a scam so as to make quick profit from it. It can automatically pop up every time you launch your web browser like Internet Explorer, Firefox, Google Chrome, Safari, etc. To achieve its purpose, it can track and store your online traces, which will violate your privacy and may steal your personal information.

How can It Come into Your Computer without Your Consent?


Usually, Checkpcinstant.com can come along with the free software downloads or online games downloads, spam email attachments, etc. besides, you may have infected by Checkpcinstant.com via visiting questionable websites, sharing malicious files with other users online, using infected external hard drive, etc.

Sunday, April 20, 2014

How to Remove Exploit:HTML/Fiexp.F Completely-Manual Removal Guide

What Is Exploit:HTML/Fiexp.F?


Exploit:HTML/Fiexp.F is classified as the Trojan Horse infection which can target almost all the windows based system. As we all know, Exploit:HTML/Fiexp.F is designed by cyber hackers to perform malicious activities on your computer and make profit from it. How can it get into your computer? Exploit:HTML/Fiexp.F can take advantage of your system vulnerability to enter into your system and modify your default computer settings to make itself active every time you launch your computer. With this Exploit:HTML/Fiexp.F operate on your computer backdoor, it can monitor your online traces and may connect to the remote server for the command, which will violate your privacy and may steal your personal information. Exploit:HTML/Fiexp.F is designed to use the rookit technology to hook deep into your system and disguise its related files onto your computer.